
Cybersecurity awareness often puts the spotlight on the systems behind the screen, such as networks, data and the AI tools now woven into daily operations. Earlier pieces in the Inside the Firewall series looked at how businesses protect data and govern AI. But security is also felt in much simpler moments, when a customer signs in, pays for an order, files a claim or asks for help. In those moments, security is no longer an IT matter sitting in the background. It becomes part of the experience itself.
That is especially true in retail, insurance and banking, where customers hand over personal and financial details in exchange for convenience and care. Every purchase, policy and payment adds to the data a brand holds, and every digital step is another place where scammers can pose as a trusted name. Fake stores, lookalike websites, hijacked accounts and fraudulent messages all target the customer directly, often outside the brand’s own channels. The tools brands rely on, from payment providers to chatbots and AI assistants, extend that exposure further.
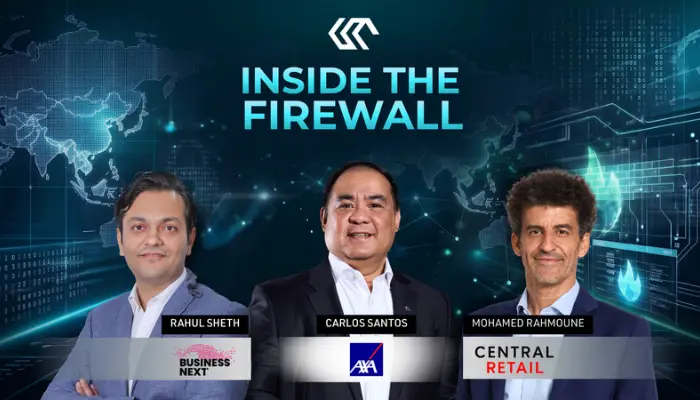
This is why personalisation and security can no longer be treated as separate decisions. The better a brand knows its customers, the more it must prove it can protect them, and the more it earns, or loses, by how it responds when something goes wrong. To explore how security works across the customer journey, this commentary brings together three leaders from customer relationship management, retail and insurance: Carlos Santos, Chief Transformation and Technology Officer of AXA Philippines; Rahul Sheth, Vice President of BUSINESSNEXT; and Mohamed Rahmoune, Chief Technology Officer of Central Retail Corporation. Their perspectives show why trust has become the new customer experience, and why security is what builds it.
The brands that win ask for less and keep it safe
For Rahul Sheth, personalisation and security used to sit in different teams. Today, customers experience them as a single decision, and every choice a brand makes about data shapes both.
“Every extra data point, such as a purchase, a location or a browsing habit, makes the experience better and gives the brand one more thing to protect. The question is no longer how much data a brand can collect, but how much it needs,” Sheth said.
That shift changes where brands should start. Instead of gathering as much as possible, the stronger approach is to collect only what is needed and treat every new data point as something to protect, not simply something to use.
Protection, he argues, has to meet customers at the moments scammers aim for.
“Scammers go where customers are, so brands need to protect people at sign-in, checkout and support. Start with strong sign-in, such as passkeys or one-time codes, and alerts when something unusual happens,” Sheth said.
He pairs the technology with people and plain speaking. AI can spot odd behaviour in real time, such as a login from a new device followed by a change to payment details, but a person should stay in the loop for tricky calls. Customers also need an easy way to freeze an account or report a fake, and a plain statement of what the brand will never ask for.
The same discipline applies to the tools around the customer. Sheth’s advice is to treat every plugin, payment tool and chatbot like a new employee: give it only the access it needs, check it before it starts and review what it does. Vendors should be asked how they store and share customer data, anything no longer in use should be switched off, and a named person should stay responsible for what chatbots and AI agents do.
Trust is where all of it is tested. The cost of an incident is easy to count, but the damage to customers is not.
“Trust is harder to count. It can take years to build and one incident to lose,” Sheth said.
Earning it back, he says, takes quick and plain communication, a fix for the cause and visible change shown through actions, not promises.
Protecting customers does not stop at the edge of a brand’s own systems, because scammers meet shoppers on fake stores and lookalike sites that borrow a trusted name. In retail, where that trust is the very thing fraudsters copy, Rahmoune, looks at what protection means beyond the brand’s own channels.
Trust is part of what is on the shelf
For Mohamed Rahmoune, personalisation and security are two sides of the same promise. Customers share data only when they trust a brand to look after it, so the old idea that more personalisation means more risk no longer holds.
“In retail, trust is now part of the product. A recommendation only feels helpful when the customer is confident about where their data is going. Without that confidence, it feels intrusive,” Rahmoune said.
The best experiences, he says, are built on less data, used better, collected for a clear reason and protected carefully.
That promise has to reach beyond the brand’s own channels. Fraudsters exploit the trust shoppers place in established names, so Rahmoune points to proactive detection of fake stores and lookalike domains, quick takedowns with platform providers, and account protection by default.
“Above all, brands should communicate consistently. Customers should know exactly how a brand will and won’t contact them, for example that it will never ask for an OTP or a password. A scam is far less likely to succeed when the customer already knows what the genuine brand sounds like,” Rahmoune said.
Every tool in the shopping journey widens that exposure, whether the brand built it or not. Rahmoune advises treating partners as part of the brand’s own estate: a clear view of every third-party tool touching customer data or payments, each assessed before onboarding and limited to the access it needs. AI chatbots deserve extra attention, and fewer, well-governed integrations are almost always safer than many unmanaged ones.
When an incident happens, the trust cost is harder to see than the financial one. Some customers simply share less, buy less or quietly move to a competitor, and recovery starts with how a brand responds in the first hours.
“Brands that are honest, act quickly and take visible ownership tend to recover. Brands that minimize or delay usually don’t. After that, recovery is earned through consistent behaviour over time rather than promises. Customers watch what you do next far more closely than what you say,” Rahmoune said.
Retail shows how trust is earned at the point of purchase, but in insurance the stakes run through the whole relationship, from buying a policy to paying premiums to filing a claim at a difficult moment. Carlos Santos of AXA Philippines, looks at what it takes to keep those digital steps safe as more of them move online.
Every claim depends on the security behind it
For Santos, insurance runs on trust, and that trust is only as strong as the security behind it. Customers entrust a provider with personal information and rely on it at important moments in their lives, so as policies, payments and claims move online, security has to be part of the promise itself.
Responsible data use, he says, goes beyond regulatory compliance. Laws such as the Data Privacy Act are an important foundation, but organisations must also keep their policies, processes and safeguards current as technology evolves.
“This means being transparent about how information is used, collecting only what is necessary, and embedding privacy and security considerations into the design of digital services. At AXA Philippines, protecting customer trust must remain central as we continue to explore how technology can improve the customer experience,” Santos said.
Scams test that security first. Scammers are getting better at impersonating legitimate companies and representatives, so insurers need to keep reminding customers of official channels and how to verify policy information and payment instructions. But awareness alone is not enough. It has to be backed by safeguards across digital services and by vetted third-party providers, particularly for payments.
“Security cannot be treated as a standalone IT concern; it must be part of how organisations evaluate new technologies, manage partnerships, and deliver services,” Santos said.
That includes clear accountability, risk checks before adopting new solutions, expectations for third-party partners and regular reviews of whether safeguards remain fit for purpose. AI brings opportunities to improve efficiency and customer service, but its use must be guided by responsible governance and data protection. For insurers, the challenge is to keep innovating while customer protection stays fundamental.
Because fraud is a shared responsibility, security also has to be easy for customers to practise.
“Preventing fraud is a shared responsibility, but organisations should make it as easy as possible for customers to protect themselves. Insurers can help by providing clear, accessible guidance on using official channels, verifying payment requests, protecting account credentials, and reporting suspicious activity,” Santos said.
The safe step should be the easiest step
Looking ahead, the three leaders point to the same test of good security: how little it asks of the customer, and how fully the brand stands behind it when something goes wrong.
For Sheth, shoppers can do their part with passkeys or a password manager, two-step sign-in and a habit of checking web addresses before paying. The design, though, is the brand’s job.
“Brands can make the safe choice the easy one: passkeys by default, clear alerts, a one-tap “this wasn’t me” button and a simple way to check that a message is genuine. The best security is the kind customers barely notice,” Sheth said.
Likewise, Rahmoune agrees that the load should not rest on shoppers alone, even if buying through official apps and never sharing OTPs help. “But the burden shouldn’t fall on shoppers alone. Brands should make the secure path the easiest one,” Rahmoune said.
As AI makes scams more convincing, he adds, brands will need to use it defensively to spot fraud patterns before customers feel them.
Meanwhile, Santos closes on what follows an incident. Prevention must always be a priority, but organizations must also be ready to respond responsibly by understanding the impact, communicating transparently, supporting customers and fixing the cause.
“Trust is reinforced not only by the safeguards an organisation puts in place, but also by how consistently it demonstrates accountability and puts customers first. At AXA Philippines, protecting customer trust must remain a continuous commitment as the digital landscape evolves,” Santos said.
**
Together, these three leaders show that a seamless customer experience is not built by removing security, but by building it deeply enough that customers never have to think about it. Sheth starts with the data itself and the case for asking for less. Rahmoune starts at the edge of the brand, where its name can be borrowed by fake stores and lookalike sites. Santos starts inside the design of the service, where privacy and security belong from the first step. Their entry points differ, but they land in the same place: the smoothest journeys belong to the brands that have already done the hard work of protecting them.
What this means for businesses is that security is no longer the cost of a good experience. It is what makes the experience possible. A quick sign-in, a one-tap payment or a claim filed in minutes only feels effortless when the system behind it can be trusted, and when something does go wrong, honesty and speed decide whether customers stay. The brands that earn loyalty will be the ones that treat a secured system as the foundation of customer experience, and the quieter that security feels to customers, the stronger it usually is.