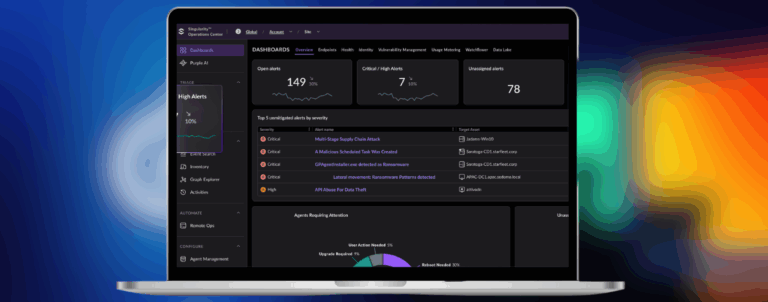

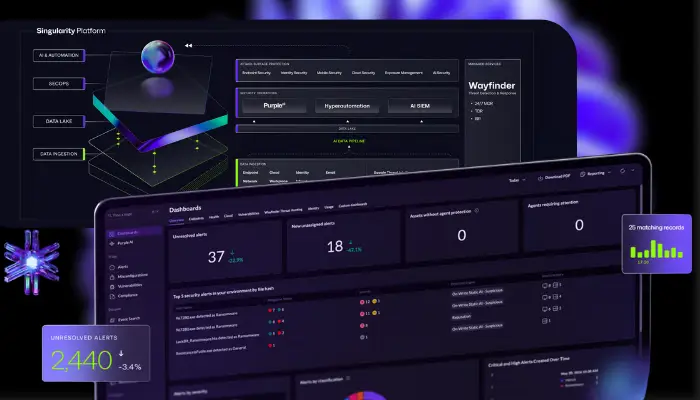
Singapore – SentinelOne has launched Singularity ASOC, an integrated suite that combines data ingestion, AI-led investigation and automated response for security operations centre (SOC) teams. The company introduced the product to its global customer conference on 27 October.
ASOC stands for Autonomous Security Operations Center. SentinelOne says the suite connects detection, investigation and response in one governed loop, with analysts setting the limits on what the system can do.
The product is powered by Purple Security Superintelligence, which SentinelOne describes as a deliberately narrow system of models built to detect, investigate and stop attacks. The company measures it against human performance on finding threats, reconstructing evidence and enabling the right action.
SentinelOne argues that human-paced work alone can no longer cover the demands on security teams. It points to rising alert volumes, thinner coverage on nights and weekends, and attackers using agentic AI to compress their timelines.
“The Autonomous SOC is not optional anymore. Attackers are using AI to move faster than any human-paced process can follow,” said Chris Corde, Chief Product Officer of SentinelOne.
Corde added, “Singularity ASOC brings Purple Agentic Investigation, AI SIEM, Hyperautomation, AI Data Pipelines and case management together as one offering on the Singularity Platform, so security teams run detection, investigation and response at machine speed, with analysts directing the work and every automated action staying inside the limits they set.”
Purple routes each task to a different model at a different point in the decision, according to the company. Behavioural and static AI on endpoints and workloads judges activity at its source and acts locally under policy, without a round trip to the cloud, while security-tuned and frontier models add context and deeper reasoning across the enterprise.
SentinelOne says it will add new model classes as each proves itself in production, including fast decision models and compact models that reason on the device. It also states that learning improves Purple over time but never allows the system to expand its own authority.
The company has shared early figures on the technology. It says Purple Agentic Investigation has completed more than 400,000 investigations of critical alerts since launch, saving customers an estimated 332,000 analyst hours.
Singularity ASOC runs on the Singularity Platform and includes five components. These are Agentic Investigation, Hyperautomation, AI Data Pipelines, AI SIEM, and threat intelligence with indicator of compromise (IOC) management.
Agentic Investigation examines alerts end to end using native and third-party security data, so analysts review findings rather than assemble evidence by hand. Hyperautomation then runs response actions and workflows from verdict to remediation.
AI SIEM applies AI to security data and includes built-in incident and case management. Threat intelligence and IOC management bring intelligence into detection and investigation, with indicators managed in one place.
For organisations that want human support alongside the software, SentinelOne’s Wayfinder service offers expert-led managed detection and response (MDR), threat hunting and incident response. The company says this extends Singularity ASOC with human judgement around the clock.
On data, native AI, endpoint, cloud and identity telemetry streams directly into the Singularity Data Lake. AI Data Pipelines then connect third-party sources to the lake and other destinations.
Every Singularity ASOC customer receives more than 50 out-of-the-box connectors to third-party sources, according to SentinelOne. These span cloud, identity, email, network, SaaS, data platforms and vulnerability management, from AWS, Google Cloud and Microsoft to Okta, Cisco, Proofpoint, Netskope, Snowflake, Atlassian, Oracle and Tenable.
The connectors also cover other security vendors’ tools, including Microsoft Defender XDR, Palo Alto Networks Prisma, Wiz, Darktrace, Sophos Central and Check Point. This lets teams investigate and respond across their wider security stack rather than only SentinelOne products.
Teams can currently ingest other sources, including on-premises systems, through syslog and Kafka. SentinelOne says OpenTelemetry and generic API collection are on the way, and that it is adding new connectors every quarter.
The pipelines can also filter and route data to third-party SIEMs and storage as well as Singularity. SentinelOne says this keeps control of data location with customers.
Tenable, one of the integration partners, said the connection brings vulnerability context into the workflow.
“Security teams can’t act on exposures they can’t see in context,” said Ray Komar, Vice President of Cloud and Technology Alliances, Tenable. “Bringing Tenable exposure data into Singularity ASOC puts vulnerability context in front of the analysts and automated workflows responding to threats, enabling teams to focus on the exposure paths attackers are most likely to exploit.”
Pricing runs through Singularity Credits, which SentinelOne describes as a unified currency customers draw down across AI-powered capabilities in the platform. Administrators set consumption guardrails, so investigations, automated actions and future agentic features run within limits the organisation defines.
SentinelOne Co-Founder and CEO Tomer Weingarten said the company is not positioning Purple as a general-purpose AI. “Purple isn’t a general superintelligence. It’s something narrower and far more useful: faster and better than any human team at one job, detecting, investigating and stopping attacks,” said Weingarten.
“In the AI era, speed is the only thing that matters, and speed without evidence just amplifies mistakes. Singularity ASOC puts Purple to work across the whole SOC, with the evidence behind every verdict and people in command of every decision it’s allowed to make,” Weingarten concluded.